Sign-in
An encrypted connection, protected passwords
Everything exchanged between your screen and the platform is encrypted: that is HTTPS, shown by the padlock in your browser. Your password, for its part, is never stored in plain text: we only keep a fingerprint of it, a code calculated from it that lets us check your password without keeping it.
- Encrypted connections (HTTPS) to the portal, the mobile app and the API
- On the portal, a sufficiently strong password required from the moment it is created
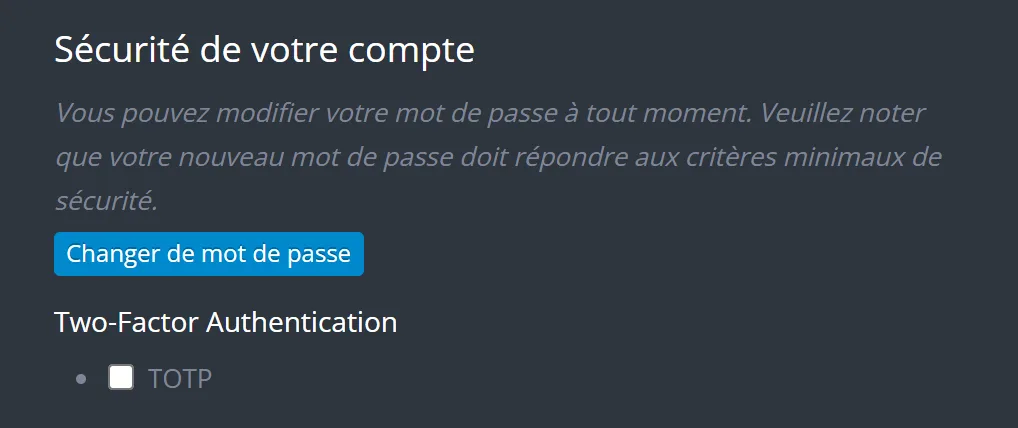
- Two-factor authentication for the web portal, which each user can choose to turn on
- Sign-in attempts in quick succession slowed down automatically
- Automatic sign-out after a period of inactivity
Two-factor authentication is a second check after your password: a temporary code, shown by an app on your phone. Once it is turned on, the password alone is no longer enough to sign in to the web portal.